Key Takeaways
- Alice & Bob estimates that a quantum computer with just 29,588 physical qubits could crack Bitcoin’s elliptic-curve cryptography in approximately one hour.
- New research from Alice & Bob, Google, and Quantinuum suggests quantum attacks could require significantly fewer resources, potentially bringing cryptographic threats closer to reality.
- Millions of BTC could be vulnerable due to exposed public keys, increasing pressure to develop quantum-resistant protections before sufficiently powerful computers emerge.
Bitcoin’s ‘Q-Day’ Threat Draws Nearer
The Paris- and Boston-based company announced Thursday that its researchers estimate a fault-tolerant quantum computer equipped with approximately 29,588 physical qubits could solve a 256-bit elliptic-curve cryptography problem in just 61.8 minutes. The mathematical problem underpins the digital signatures used to authorize bitcoin transactions.
The findings, detailed in a new research paper, also suggest that 22,593 physical qubits could break RSA-2048 encryption in approximately 3.14 days, a significant reduction from earlier estimates. In 2019, researchers projected that factoring RSA-2048 would require roughly 20 million physical qubits, while a revised estimate from Google Quantum AI last year brought that figure below one million.
Alice & Bob says its latest calculations represent a new benchmark for minimizing the combination of quantum hardware requirements and processing time.
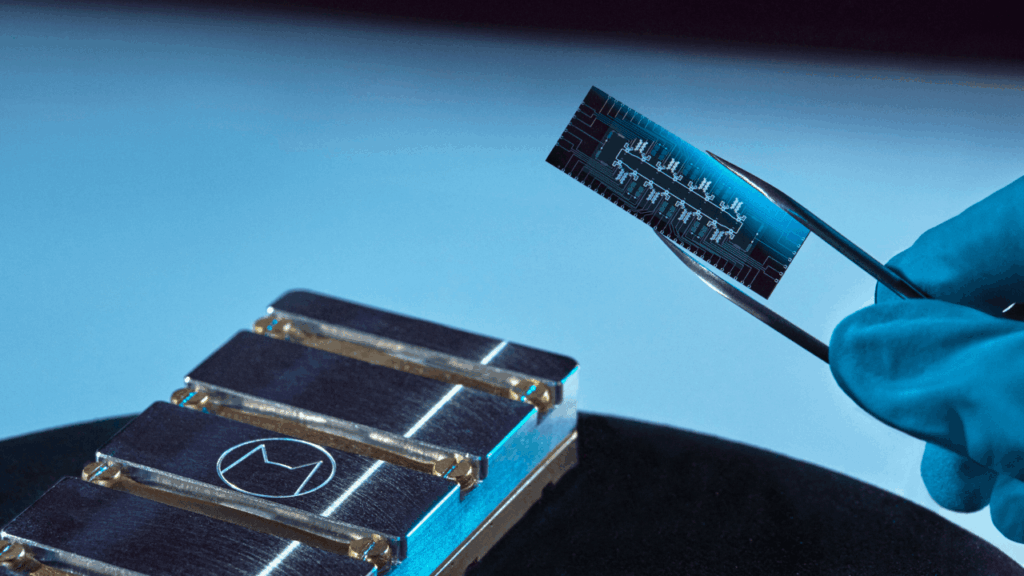
The research relies on a specialized superconducting technology known as cat qubits, designed to reduce certain quantum errors at the hardware level. Researchers combined that approach with more efficient error-correction codes and improvements to the mathematical operations required by Shor’s algorithm, the quantum computing method capable of defeating widely used public-key cryptography.
The company emphasized that its findings are theoretical resource estimates rather than evidence that existing quantum computers can crack bitcoin keys. Building machines capable of reliably performing these calculations remains a major engineering challenge.
For Bitcoin, the implications center on its elliptic-curve digital signature system, which allows users to demonstrate ownership of funds. A sufficiently powerful quantum computer could potentially calculate private keys from exposed public keys, enabling attackers to generate unauthorized signatures and steal cryptocurrency.
Alice & Bob’s estimated one-hour attack would still exceed Bitcoin’s roughly 10-minute average block interval, limiting the immediate practicality of attacking ordinary transactions while they await confirmation. However, coins associated with already-exposed public keys could face a more serious threat because attackers would not necessarily need to complete the calculation before the next block.
The Pace Is Accelerating
The announcement follows a series of recent developments suggesting that the technical barriers to quantum attacks are gradually diminishing.
As Bitcoin.com News reported earlier this month, Google Quantum AI demonstrated an error-reduction technique called magic state cultivation, achieving a 40-fold improvement in the reliability of specialized quantum states required for complex calculations. Separate Google research published in March suggested that an advanced quantum machine could theoretically compromise Bitcoin’s elliptic-curve signatures using fewer than 500,000 physical qubits, with one proposed configuration completing an attack in approximately nine minutes.
Meanwhile, quantum computing company Quantinuum announced on Oct. 19 that its Helios system had reached 99.9995% logical fidelity, equivalent to approximately five errors per million operations. The company described the achievement as supporting its ambitions to deliver a commercially useful fault-tolerant quantum computer by 2029.
Alice & Bob’s calculations represent a different kind of progress, demonstrating how architectural choices and improvements in algorithms could substantially reduce the equipment needed to attack existing cryptographic systems.
“Estimates of the resources needed to run the algorithm have been steadily falling as the field has developed better approaches to error correction and algorithm design,” said Alice & Bob CEO Théau Peronnin, in a statement.
The company expects improving quantum hardware and declining computational requirements to potentially converge in the early 2030s, although that remains a projection rather than an established timeline.
The findings add pressure on Bitcoin developers to investigate quantum-resistant signature schemes before such machines become available. Previous estimates suggested approximately 6.9 million BTC could face potential exposure because the corresponding public keys have already been revealed.
Replacing Bitcoin’s existing signature technology would introduce considerable complications, including larger transaction data requirements, compatibility issues with existing wallets, and the difficult question of how to protect coins held in inactive or inaccessible addresses.
Alice & Bob urged organizations to begin adopting post-quantum cryptographic protections rather than waiting for a working quantum attack.
For Bitcoin, where changes require extensive technical review and broad network coordination, the shrinking estimates could make preparation increasingly important, even as the practical arrival of a cryptographically capable quantum computer remains uncertain.